
You can always tell who does real IT work in these threads lol
Is it standard practice to release the security updates on GitHub?
I am a very amateur self hoster and wouldn’t go on the github of projects on my own unless I wanted to read the “read me” for install instructions. I am realizing that I got aware I needed to update my Jellyfin container ASAP only thanks to this post. I would have never checked the GitHub.
Not really.
Depending on how you install things, the package maintainers usually deal with this, so your next
apt update/pacman -Syuvor … whatever Fedora does… would capture it.If you’ve installed this as a container… dunno… whatever the container update process is (I don’t use them)
I indeed use a container. Wasn’t familiar with the update process for containers but now know how to do it.
There’s a lot of good container management solutions out there that are worth investigating. They do things like monitor availability, resource management, as well as altering on versioning.
If you haven’t already, I recommend Watchtower (nickfedor fork—the original is unmaintained) which automatically pulls updates to Docker containers and restarts them. Make sure to track latest, although for security updates, these should be backported to any supported versions so it’s fine to track an older supported version too.
Lol it’s already insecure then. Don’t bother.
Implying you have access to some major Docker 0-day exploit, or just talking out of your ass? Because a container is no more or less secure than the machine it runs on. At least if a container gets compromised, it only has access to the volumes you have specifically given it access to. It can’t just run rampant on your entire system, because you haven’t (or at least shouldn’t have) given it access to your entire system.
Docker is known insecure. It doesn’t verify any layers it pulls cryptography. The devs are aware. The tickets remain open.
I don’t know if I remember correctly but I could not install Jellyfin on the latest Ubuntu server version. I had to use docker to get Jellyfin running.
If that is indeed true it would only mean that the docker container is vulnerable to a supply chain attack. You are not any more vulnerable to a vulnerability in the codebase.
If you’re using the ghcr image, to post malicious code there, the attack would have already had to compromise their github infra … which would likely result in the attacker being able to push malicious code to git or publish malicious releases. Their linux distro packages are self published via a ppa/install script, which I would assume just pull from their github releases, so a bad github release would immediately be pulled as an update by users just as fast as a container.
Insane way of thinking.
Unattended upgrades set to security only and never worry
It’s difficult to do security-only updates when the fix is contained within a package update.
Even Microsoft’s security updates are a mix with secuirity updates containing feature changes and vice versa.
I usually do an update on 1 random device / VM and if that was ok (inc. watching for any
.pacnewfiles) and then kick Ansible into action for the rest.Why does unattended upgrades with security only setting not fix this?
This is literally why Debian has distinct repos for security updates.
Let me know which repo this update appears in.
Is it standard practice to release the security updates on GitHub?
Yes.
And then the maintainers of the package on the package repository you use will release the patch there. Completely standard operation.
I recommend younto read up on package repositories on Linux and package maintainers etc.
The Jellyfin has an official Telegram channel which I use as the newsletter.
Besides that, the selfh.st newsletter usually highlights the more popular projects if such an issue arises.I am realizing that I got aware
I don’t run the arr stack, but this is key. You really should do your due diligence before you update anything. Personally, I wait unless it’s a security issue, and use all the early adopters as beta testers.
Just updated, thanks for the info <3
If only 10.11 were usable for me at all.
What’s the issue?
In addition to the other comment, it currently has some pretty rough performance issues with big libraries.
There was a regression that caused Jellyfin to be a LOT more restrictive regarding the structured filesystem format. But this could be something else
It’s probably database performance related. There’s a massive PR undergoing round after round of reviews that, when merged, will be a change to 10.12 and will resolve all of the new database performance issues experienced in certain edge cases (book libraries, large music libraries, large collections, etc)
I don’t have books, moved music to navidrome, and have a relatively small library and it just will not play nice. Library scans lasting for days kind of nasty. RAM and CPU domination.
Yeah this is unfortunate news for me as well. I have a primary container I use for videos, and then a 10.10 server for music. 10.11 is borderline unusable for music for me, and I’ve tried everything for rescanning to completely redoing the server set up (rip accidentally deleting all my music playlists).
But i shall kill off the 10.10 container and hope a performance fix is in the works.
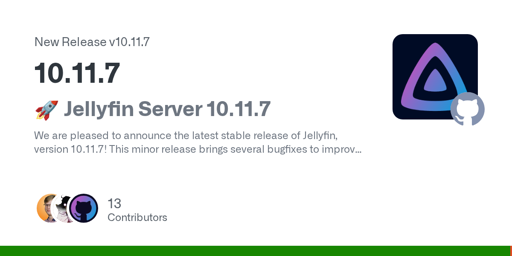
That changelog just screams AI lol. All the emojis
Three. Three emojis, used in headings as a bullet point.
It is perfectly plausable for someone whos job is to write technical documentation and promotional material would punch it up with a couple 'mojis.
https://github.com/jellyfin/jellyfin/releases
Every single release uses the same format with the same 3 emojis. You’d know that if you’d clicked “releases” and had even a modicum of curiosity.
It isn’t, not that I would care anyways
No worries. We’ve been communicating with pictures since ancient cave men scrawled pictographs on cave walls with a piece of burnt firewood.
I forgot that it’s April first, and was wondering what catasthropic event had happend in order that it had to be stated in the title that its not a joke
The update rolled out perfectly for my Kubernetes setup (using the Docker image). 👍
Just a reminder that you should never expose Jellyfin to the internet
The worst part of enthusiast threads are the “I am very smart” takes like this
You objectively shouldn’t expose Jellyfin to the internet. It has a rather large attack surface and isn’t designed with security in mind.
Pretending everything is fine won’t solve the problem
Sounds like a great reason to use Plex instead!
edit: to add something constructive to my snarky comment, what kind of attack surface are we talkin here? Multiple ports? Lots of separate services running?
Plex has its own set of problems
Sure, but being mostly secure by default isn’t one of them. One advantage of running a service that offers optional subscription services is that they can offer security features like built-in SSL and AAA that just work. Any average user can install it and have a reasonably secure service running. Hell, until a few months ago you didn’t even need to open a port to have remote access to your content, whether you paid or not. Now they’ve made that a paid feature though.
There has been a known “anyone can access your media without authentication” vulnerability for seven years and counting, and the Jellyfin devs have openly stated that they have no intentions of fixing it. Because fixing it would require completely divesting from the Enby branch that the entire program is built upon. And they never plan on refactoring that entire thing, so they never plan on fixing the vulnerabilities.
The “don’t expose it to the internet” people aren’t just screaming at clouds. Jellyfin is objectively insecure, and shouldn’t be exposed.
Jeez, so it’s meant to be a literal home media server lol. Able, but not designed, to be used for sharing.
Exactly. And that’s honestly why I doubt it will ever truly contend with Plex. It’s fine for sharing with friends who can figure out how to connect via VPN, but it’ll never be robust enough to share with your tech-illiterate grandparents on the open internet. Plex wins handily in that regard, because their sign in process is basically the same as Netflix, HBO, Hulu, etc…
Plex has problems of its own, but (at least as of me writing this) it doesn’t have any major known security vulnerabilities. They had some level 10.0 vulnerability last year, but they followed standard CVE protocols and patched it before the vulnerability was actually released.
Ahh bummer. It works so well as a home media server… kind of calls out for sharing.
yeah okay let me just connect grandma’s tv to a vpn.
Setup a VPN gateway at Grandma’s house. Works fine for me.
I think you’re missing the point - that’s neither simple nor easy for most people. I’m a network engineer and I don’t wanna deal with setting up and (being responsible for troubleshooting) a bunch of VPNs! Nevermind the additional power/CPU usage from the tunnels. My parents just got fiber and they don’t even have a public address (ipv4 or v6) which just adds another layer of headache. thanks west virginia…
If you have the skills to setup a Jellyfin server you also have the skills to setup wireguard.
My parents just got fiber and they don’t even have a public address (ipv4 or v6) which just adds another layer of headache. thanks west virginia…
That’s a very specific use case.
I’d much rather deal with setting up a few VPN gateways which is trivial at most…than securing a public web service. I deal with that crap enough at work.
There are a lot less variables to contend with with a single VPN endpoint which undergoes considerably more security auditing than N public web services. Many of which I don’t have the time to review myself and mitigate if they decide to suck at coding.
Edit: I share my services with less than 5 households though.
Edit2: I’m not sure what public ipv4 or ipv6 has to do with this. My remote sites use starlink ipv4. I haven’t setup ipv6 on those internally at all. They all tunnel via wireguard to my homesite.
also fyi starlink has public ipv6 available if you DO wan’t to set it up. been hosting a minecraft server off a starlink connection lol.
When I set up wireguard it was just more complicated when one side didn’t have a public IP. Whyyyy can’t we adopt ipv6 already.
There are plenty of ways around this
A cheap minipc is only like 20-40 USD and would solve the problem overnight
I can set it up, and you can set it up, but for the average user?
The average user isn’t using Jellyfin
All you need is a little Linux knowledge in order to setup Netbird with Caddy
I’m talking average enough to see an article, or hear about it from a friend/coworker, then follow the insanely easy setup directions for Windows. I know plenty of people who aren’t really “computer people” but know enough to open a port because they had to to get a game working at some point or another. Those people probably wouldnt notice “hey this thing is going to http maybe i should rethink this…”

These are going to be the people who think it’s smart to just open up RDP and SSH to the wide web though…they shouldn’t be forwarding ports…they should use a VPN.
I had to explain to one of them why RDP is a bad idea lol. Thats kind of my point - average people tend to only know enough to be dangerous, not to do things safely. Or as Shakespeare said - "The fool doth think he is wise, but the wise man knows himself to be a fool.”
Are you singling out Jellyfin for a particular reason? Or are also going to advise just never opening ports in general?
For the vast majority of users? Yes. They shouldn’t forward ports.
Setup a VPN gateway at Grandma’s house.
Jellyfin is particularly bad compared to other things. You still should avoid exposing stuff to the internet
jellyfin people just always spout this advice as some sort of copium and i dont even know why. ALL software will have security issues at some point or another. just update and move on with your life.
That’s kinda my perspective on it to. I mean, how do they think websites work? Gotta expose ports to make all the internet things happen. Sure commercial stuff will have more devices to protect it, but there are things you can do to mitigate issues at home too.
There is a new story every week in Steve Gibson’s “Security Now” podcast about why you should virtually never open ports. And if you do, you’d better IP restrict. Even, or especially, in commercial products. Cisco has a new CVSS 10.0 every other week just about
I run pretty much all my stuff through NPMplus. Then I have a firewall between my public and private networks in case something does get compromised. But I’ve had Plex exposed (on a non-default port) for literally years and nothing ever happens.
Why NPMplus and not the default NPM?
Primarily for the CrowdSec integration (one less thing to set up manually)
Why link the fork of a fork in your original response?
Definitely.
But I think more than copium it’s them understanding their users. It’s advice for people that will figure out how to run Jellyfin but won’t stay on top of updates, setup a waf, use a firewall/reverseproxy to limit access, etc. There are surely a lot of those that just one clicked an installer etc and for them it’s good advice.
that’s fair, does it not have any kind of encryption by default?
Standard TLS, I think, but what else would you need?
None really, just wondering what the issue with opening it up is if it has TLS? In 10+ years I’ve never had my Plex server compromised and it just uses TLS. I do change the default port but that’s it.
Plex logins go through their login server so you’ll also have login throttling and probably other bot protections.
Thanks for this post, i would have updated mine next semester…
There is a good reason I only have Jellyfin and other services accessible via valid Client Certificate.
Also interested how this works for mobile apps. I self host a number of services through caddy as my reverse proxy but each application is just dependent on it’s own authentication. If I exposed all my services to the internet, that’s a huge attack vector. If anyone else has some ideas I’d be happy to listen.
If you are the only user and don’t need to use those apps in devices you don’t own a vpn is the way to go.
If not. Depending the number of users you could do some heavy ip geoblocking to at least reduce the exposed surface.
There are a few services I have just like 3 IPs allowed to get a response from caddy, any other ip gets 403 error.
Does it work with android and TV apps?
I tried long ago and failed.
No, we only use Jellyfin via browser. Unfortunately even with imported Client Cert, Android apps won’t work.
Edit: Client Certs need to be implemented per App. There is a feature request from 2022 https://features.jellyfin.org/posts/1461/capability-to-specify-client-certificate-for-android-client
thanks for posting this!
In the raspian repos, just updated, thanks.
also in the docker repository.
Acronyms, initialisms, abbreviations, contractions, and other phrases which expand to something larger, that I’ve seen in this thread:
Fewer Letters More Letters HTTP Hypertext Transfer Protocol, the Web VPN Virtual Private Network nginx Popular HTTP server
[Thread #203 for this comm, first seen 1st Apr 2026, 09:50] [FAQ] [Full list] [Contact] [Source code]
Removed by mod
I know you’re gatekeeping from Turd Mountain, but just for completeness, the reason I use Jellyfin besides the “pretty for my wife” reason is that it keeps track of her progress between clients. She sometimes watches things on her laptop, sometimes her phone, sometimes her tablet, and sometimes the TV, and no matter which one she uses it’ll remember which episode of her show is the next episode. It also highlights when a new episode of something has been added and cues her to watch the new episode that just came out.
But yeah, if I was alone and only had a pile of anime I’d already seen before, which I only watched from my Linux devices, Samba and VLC would do me fine 😛
But yeah, if I was alone and only had a pile of anime I’d already seen before, which I only watched from my Linux devices, Samba and VLC would do me fine 😛
Use NFS for your sanity. Linux samba/CIFS is annoying to deal with.
Also, mpv
Honestly, I’m not a big fan if Microsoft generally, but I found NFS to be surprisingly not great for non-permanent infrastructure, whereas SMB took a few minutes and works great, at least in my use cases. Maybe I’m just a loser, though.
Nah, if it works for you then use it. There are no rules here!
Nope? how about fancy stuff GUI and plot?
IMDB on your phone I guess…Am I having a stroke?
At the time off writing you made a few more comments, so either “no” or “yes but your life is Lemmy”.
Do you smell burning fish?
Im on fedora and I have installed through dnf, no updates with the dnf update… should I wait?
I depends a bit on your threat model. If you have Jellyfin exposed to the internet I would shut it down immediately. If you are running locally and rely on it, let it run maybe? If behind a tailnet or some other VPN, I would deactivate it as well. If it is an Axios like vulnerability it may be possible your secrets are in danger, dependent on how well they are secured. Not a security expert, but I would handle this a little more conservative…
No need to shut it down if it’s not exposed to the internet. Tailnet/VPN is fine.
If it’s a supply chain compromise shutting it down wouldn’t matter. The damage is already done.
I don’t believe it a supply chain compromise
It’s on my home, which is not 24/7 open. Will see check later.